WordPress application passwords are a security feature that allows third-party services to connect to your website when making REST API requests. Introduced in WordPress 5.6, they solved the messy authentication process that previously relied on cookie-based methods, which were unreliable and vulnerable to attacks.
How They Work
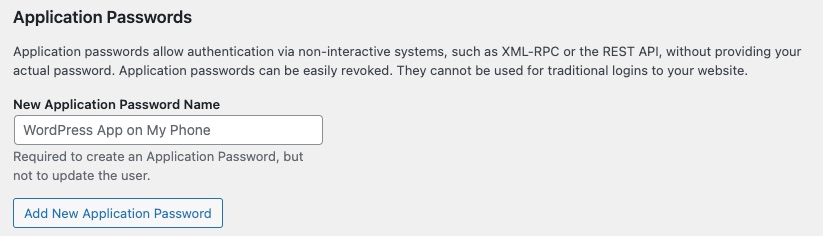
Think of application passwords as special keys you can create for different apps that need access to your site. Instead of sharing your main WordPress login credentials, you generate unique passwords for each service. This way, if one gets compromised, your main account stays safe.
The system makes it easy to generate these passwords through your WordPress dashboard. You simply go to Users > Profile, find the Application Passwords section, and create a new one by giving it a descriptive name. Each password is tied to a specific application, making it simple to track which services have access to your site.
The Good and Bad
Application passwords offer several advantages. You can easily revoke individual passwords without affecting others, track when they were created and last used, and maintain better security through features like two-factor authentication and reCAPTCHA.
However, they’re not perfect. Your site remains vulnerable to brute-force attacks where hackers try different password combinations. It’s also difficult to control which user roles can create these passwords, and there’s limited logging to monitor their usage.
Should You Use Them?
If you don’t need third-party applications connecting to your WordPress site through APIs, many security experts recommend disabling application passwords entirely. You can do this manually by adding a simple code snippet to your functions.php file, or by using security plugins like Wordfence or WP Cerber Security.
For sites that do need API access, application passwords remain a much safer option than the old authentication methods.
