Cookies are files that store the user’s browsing data on a website. They are commonly used to store the user’s login details, pages visited, items added to the shopping cart, and more.
Marketers also use cookies to learn about user browsing behavior and experiences so that they can develop a better marketing strategy. For privacy reasons, users can delete cookies in their web browser.
In WordPress, there are 2 types of cookies by default – session cookies and comment cookies. The former are set when someone logs in to your website with an email and password or with a password only. The latter save the email, user name, and URL as soon as a user leaves a comment.
WordPress expires the login cookies every 15 days, but it takes 347,222 days or 30000000 seconds for the comment cookies to be deleted from your database.
How password protection works in WordPress
WordPress has a built-in feature that allows you to lock your website. When you protect your pages or posts, they will have a password form that forces visitors to enter the correct password in order to read the content.
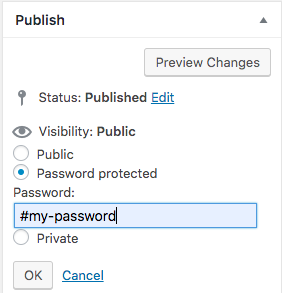
By default, WordPress stores the password in a cookie that expires 10 days after it is created. If you lock multiple pages with one password, users only have to enter the password once and can see all other private content.
This means that WordPress has saved their cookies and sends them directly to the secure content without asking them to fill out the password form.
How to change the expiration time of password cookies in WordPress
There are several reasons why you might want to adjust the cookie expiration time. You offer a one-day event via a password-protected site and want users to access it only on that day.
To do this, you need to add the post_password_expires filter to your WordPress functions.php file. The process works as follows.
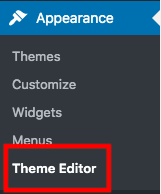
In your WordPress dashboard, go to Appearance → Theme Editor.
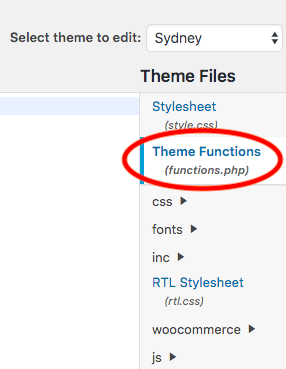
In the left navigation menu, click on the functions.php file with the theme functions.
Paste this code into the file:
function mind_set_cookie_expire( $time ) {
    return time() + 86400; // 1 day
}
add_filter( 'post_password_expires', 'mind_set_cookie_expire' );
Once this is done, update the file. In line 2 we use seconds for the return time. You can replace it with your own time span.
This method is suitable for those who are familiar with programming. It would be a challenge for those who are not technically inclined. We recommend that you use the Password Protect WordPress Pro plugin to easily customize the password cookie expiration time. It will also provide you with numerous other useful and powerful features.
Use Password Protect WordPress Pro to change the cookie time for password protected pages in WordPress
The PPWP plugin secures your WordPress pages, posts, and custom post types with one or more passwords. It supports categories, parent and child pages as well as protecting the entire website.
In addition, you can set a cookie expiration time on the plugin’s settings page, during which users do not have to re-enter their passwords to view the private content.
These 3 steps will help you get started with the plugin.
Download the PPWP Pro plugin. In your WordPress administration, go to Plugins → Add new.
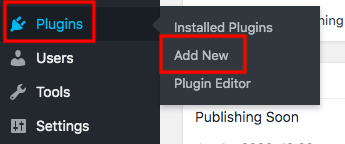
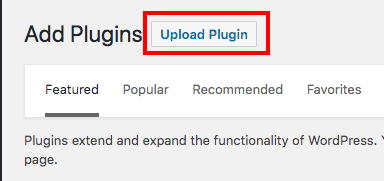
Click on Upload plugin and open the downloaded zip file of the plugin. Enter the license key that was sent to you by email and activate the plugin.
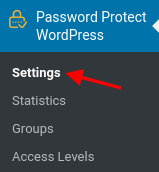
Visit the Password protection for WordPress settings page. Search for the option Cookie expiry date.
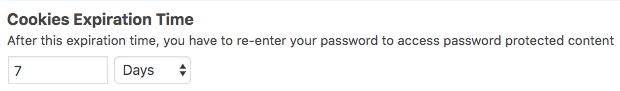
Set a day on which the user cookies expire. The default time is 7 days. Save your changes.
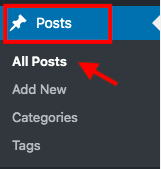
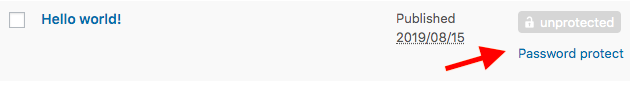
Please note that this cookie setting only applies to protected content. You must therefore set a password for your pages or posts. This guide shows you how to lock your content with the plugin. Go to the Pages or Posts section in the WordPress backend navigation menu.
Select the desired post. Click on the Password protection link and then on the Password protection button for this page.
Generate a password automatically or create your own.
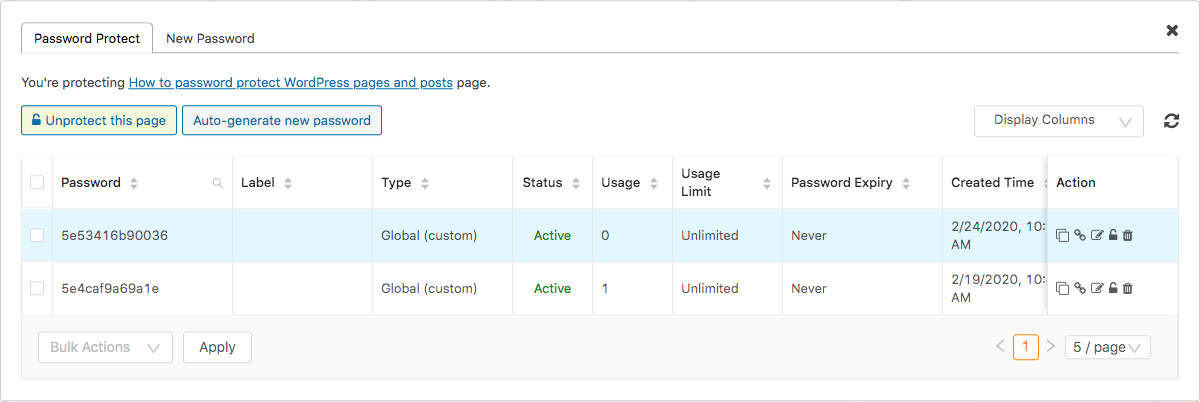
Restrict password use
PPWP Pro Plugin proves to be a powerful and efficient way to manage your passwords. You can expire your passwords by usage or time period. The automatically generated passwords remain forever until you delete them.
On the other hand, you can set customized usage restrictions and expiry times for specific passwords. This means that users can no longer use this password once it expires.
Grant direct access to user roles on the whitelist
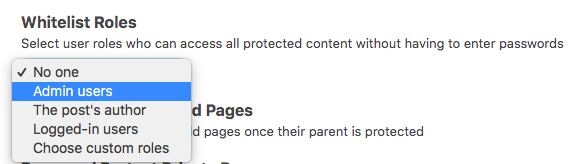
Another reason for using WordPress cookies is to whitelist roles. For some regular users, such as admins or editors, it is not necessary to log in again or enter passwords to access their content.
For this reason, PPWP Pro offers the “Whitelisted Roles” function, which allows you to give certain user roles the right to open protected content without having to enter passwords.
To do this, simply select the desired roles directly on the PPWP Pro settings page.
Use password-protected pages and cookies of WordPress
WordPress saves user password cookies and allows them to read your protected content without having to re-enter their passwords in 10 days.
You can take 2 different routes to change the default cookie expiration, either by adding code to the functions.php file or by using the Password Protect WordPress Pro plugin. The first method requires a bit of coding, while the other is only available in the paid version.
You can do quite a lot with PPWP Pro. In addition to protecting pages and posts, you can protect an entire category and the entire website with just a single click.
Install Password Protect WordPress Pro and set a custom time limit for page cookies for your protected WordPress content.
