Failed login attempts on your WordPress site might seem like no big deal, but they can actually signal serious security problems. Sometimes, it’s just people mistyping their passwords, but other times, it’s automated bots trying to break into your site.
The difference between harmless typos and malicious attacks can make or break your website’s security. Here’s how to identify what’s happening and what to do about it.
What causes failed login attempts?
Failed login attempts happen when someone tries to access your WordPress site with incorrect credentials. This could be the wrong username, wrong password, or both.
Legitimate causes include:
- Password typos from real users
- People forgetting their login details
- Users trying old passwords after you’ve changed them
Malicious causes include:
- Brute force attacks where bots try thousands of password combinations
- Targeted attacks against specific user accounts
- Automated scripts probing for weak security
A few failed login attempts here and there aren’t a problem. But when you see dozens or hundreds in a short period, that’s usually a sign of automated attacks.
These attacks can slow down your website by consuming server resources and bandwidth. If attackers actually succeed in getting access, they can steal data, inject malware, or redirect your site to malicious content. Google notices these problems and can penalize your search rankings or even blacklist your site entirely.
Even legitimate failed logins can hurt user experience if people get frustrated and leave your site.
7 ways to handle failed login attempts
WordPress doesn’t have built-in protection against excessive login attempts, but there are several approaches you can take to address the problem.
1. Add password visibility toggles
One of the simplest ways to reduce legitimate failed logins is to let people see what they’re typing. Most modern websites include a little eye icon that lets users toggle password visibility.
This helps people catch typos before they submit the form, especially on mobile devices where typing can be more error-prone. Many WordPress security plugins include this feature, or you can add it with custom code or specialized plugins designed for password management.
Here’s how you can customize your password forms per your tastes with PPWP and WordPress Customizer.
- In your WordPress dashboard, go to Plugins > Add New. Look for PPWP in the plugin search box. Install and activate the plugin.
- Go to Appearance > Customize > PPWP Sitewide Login Form.
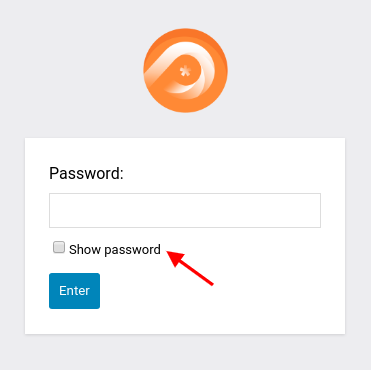
- Navigate to Password Reveal Button. Switch on the “Enable Password Reveal Button” option. You can also fill in your own custom button text and decide the button color.
This is how the login form looks after enabling the password reveal button with PPWP plugin.
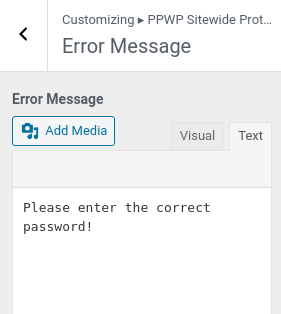
For custom error messages, head to the Error Message section and enter your unique message, then hit Save.
2. Create bypass links for trusted users
If you’re running a private or membership site, you can create special access links that let trusted users bypass the login form entirely. These links can be set to expire after a certain time or number of uses.
This approach works well for client sites, staging environments, or any situation where you want to give specific people access without requiring them to remember login credentials.
3. Use strong login credentials
This might seem obvious, but many WordPress sites still use weak usernames and passwords. Strong credentials make brute force attacks much less likely to succeed.
Your password should be at least 12 characters long and include a mix of uppercase letters, lowercase letters, numbers, and special characters. Avoid using “admin” as your username, and don’t use easily guessable information like your business name or birth year.
Consider using a password manager to generate and store complex passwords for all your accounts.
4. Keep WordPress updated
WordPress regularly releases security updates that patch vulnerabilities that attackers might exploit. Running an outdated version makes your site an easier target.
The truth is that less than 60% of WordPress sites run the latest version, which means a huge number of sites are unnecessarily vulnerable to known security issues.
Set up automatic updates for minor releases, and make sure to test and apply major updates promptly. If you’re running an older version, consider hiding your WordPress version number from public view to make it harder for attackers to identify potential vulnerabilities.
5. Limit login attempts
WordPress allows unlimited login attempts by default, which makes brute force attacks possible. Installing a plugin that limits login attempts can stop these attacks in their tracks.
The Limit Login Attempts Reloaded plugin is a popular choice that lets you:
- Set a maximum number of login attempts per IP address
- Configure lockout periods for blocked IPs
- Display remaining attempts to legitimate users
- Get email notifications about blocked attempts
- Maintain allow/block lists for specific IPs or usernames
Some hosting providers, like WP Engine, include login attempt limiting as part of their security features, so check whether you already have this protection before installing additional plugins.
6. Choose secure hosting
Your hosting provider plays a big role in your site’s security. Cheap shared hosting might save money upfront, but it often lacks the security features you need to protect against attacks.
Shared hosting means your site shares server resources with potentially hundreds of other websites. If one of those sites gets compromised, attackers might be able to access other sites on the same server, including yours.
Look for hosting providers that offer features like:
- Server-level security monitoring
- Automatic malware scanning
- DDoS protection
- Regular security updates
- Isolated hosting environments
7. Enable two-factor authentication
Two-factor authentication (2FA) adds an extra security step that makes it much harder for attackers to access your site even if they guess your password.
With 2FA enabled, users need to provide a second form of verification – like a code sent to their phone or generated by an authenticator app – in addition to their username and password.
The WP 2FA plugin is a solid free option that supports multiple authentication methods including time-based codes, email verification, and SMS. Many all-in-one security plugins like Wordfence and Jetpack also include 2FA features.
Monitoring and responding to attacks
Setting up protection is just the first step. You also need to monitor your site for signs of ongoing attacks and respond appropriately.
Check your server logs regularly for patterns of failed login attempts from the same IP addresses. Most security plugins provide dashboards that make this information easy to review.
If you notice a coordinated attack, consider temporarily blocking the attacking IP addresses at the server level. For large-scale attacks, your hosting provider might need to implement additional protections.
Conclusion
If you’re seeing persistent attacks that your current security measures can’t handle, it might be time to bring in professional help. Web security companies can provide advanced protection services, and experienced WordPress developers can audit your site’s security configuration.
Don’t wait until an attack succeeds to take action. The cost of recovering from a successful hack – including lost data, downtime, and reputation damage – is usually much higher than the cost of implementing proper security measures upfront.
Most failed login attempts fall into predictable patterns once you know what to look for. Legitimate users make occasional mistakes but don’t typically retry dozens of times in quick succession. Automated attacks often target common usernames like “admin” and try password combinations in systematic patterns.
By implementing a combination of these security measures, you can reduce both legitimate failed login frustrations and malicious attack attempts, creating a more secure and user-friendly experience for everyone who needs to access your WordPress site.
